Skip to content

ABOUT

A boutique offensive security and secure-solutions firm.

PROFOSS is built on verified vulnerability research, international bug bounty rankings and hands-on engineering. You work directly with the specialists who test and build.

OUR NAME

Order then. Insight now.

The name comes from 17th-century Sweden. A profoss was an appointed authority responsible for order, discipline and security.

Today, we carry that same uncompromising mindset into the digital realm: to examine, question and understand what others need to be able to trust.

Through offensive cybersecurity and secure solutions, we find the weaknesses – and help engineer them out.

With precision, evidence and a clear purpose.

— PROFOSS — KNOW YOUR EXPOSURE.

The name is our inspiration, not our history. PROFOSS makes no claim of connection to any historical institution.
We combine offensive security with hands-on engineering. We examine systems through an attacker's eyes – and we can also roll up our sleeves and build secure solutions.

Engage us for what you need: a penetration test, a secure solution or both. The approach is shaped around what you want to achieve.

HOW WE WORK

Careful scoping
A test is only as good as the question it answers. We take time to understand what you need to know.
Responsible testing
We work within agreed boundaries and respect operations and business continuity.
Clear communication
Straight answers, without drama and without unnecessary jargon.
Confidential handling
Information about your environment is treated restrictively during and after the engagement.
Actionable reporting
Findings are written so those remediating understand what, why and how.
Respect for reality
Engineering teams have deadlines and businesses have constraints. Recommendations take that into account.

THE PEOPLE BEHIND PROFOSS

Technical experience. Personal accountability.

PROFOSS is operated by two security professionals. You speak directly with the people carrying out the assessment.

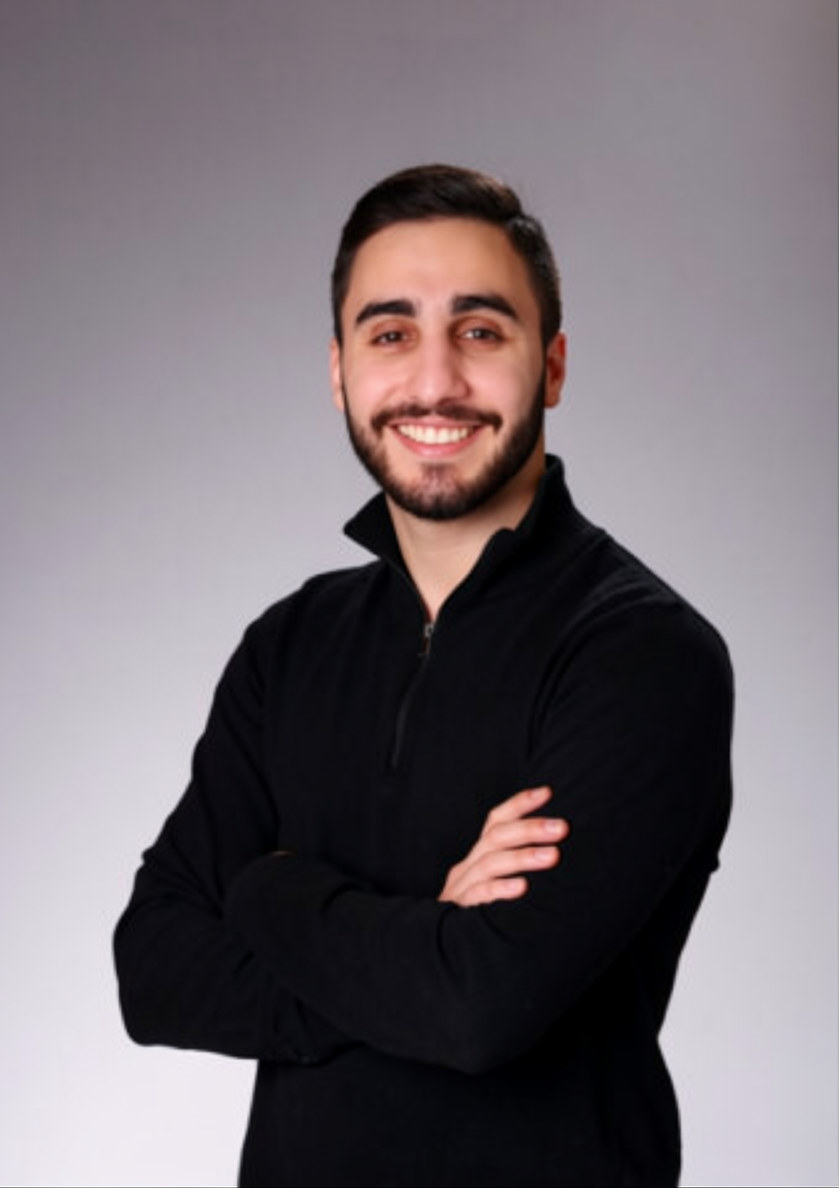
Portrait of Zagros Bingöl

Zagros Bingöl

Chief Hacking Officer — Co-founder

INDIVIDUAL CERTIFICATIONS

  • Blue Team Level 1

    Blue Team Level 1

    Security Blue Team

  • Junior Penetration Tester

    Junior Penetration Tester

    INE

  • CCNA Routing and Switching

    CCNA Routing and Switching

    Cisco

  • Multi-Cloud Red Teaming Analyst

    Multi-Cloud Red Teaming Analyst

    CyberWarFare Labs

  • Certified Appsec Practitioner

    Certified Appsec Practitioner

    SecOps Group

  • Certified Appsec Pentester

    Certified Appsec Pentester

    SecOps Group

Zagros Bingöl is an offensive cybersecurity specialist with experience spanning penetration testing, security operations and IT infrastructure. His background combines offensive testing with defensive security, providing a practical understanding of how vulnerabilities affect organisations and how remediation reduces risk.

As a penetration tester at Combitech, Zagros assessed web applications, APIs, infrastructure, Active Directory, AWS, mobile applications and IoT environments. His work included white-box, grey-box and black-box testing.

He previously worked in a Security Operations Centre, gaining experience in security monitoring, threat investigation and defensive security operations.

At PROFOSS, he focuses on identifying security weaknesses through practical testing, validating findings with evidence and delivering clear, actionable recommendations.

TECHNICAL FOCUS

  • Applications & APIs
  • Infrastructure & Active Directory
  • Cloud environments
  • Vulnerability research

NEXT STEP

Let’s start with your security objectives.

Tell us what you want to test, build or improve. We will suggest a suitable approach and explain the next steps.